
Meta Fined $25 Billion for Improper Sharing of User Data
New Mexico fines Meta $25 billion for data privacy violations linked to Cambridge Analytica, underscoring impact on enterprises under data-protection laws

Tor Exit Relays Hijacked, Banks Detect Rogue AI Agents, Self-Rebuilding macOS Ransomware
Heartbreaker macOS ransomware self-rebuilds, but a hardcoded AES key and reliance on scarce Rust limit its current threat level
Hackers Breach Enterprise Firewalls and VPNs, Exposing 70,000 Credentials
Global campaign targets exposed edge devices, exposing over 70,000 credentials and enabling persistent access across multiple regions
Mirai Botnet Operators Expand PHP2Shell Attacks as ASLR Bypass Exploits Emerge
Mirai-botnet attempts via PHP2Shell exploit; ASLR bypass revealed, but no confirmed breaches as patches roll out globally
Quest Diagnostics Confirms Data Breach Exposed Patient Records
Quest Diagnostics confirms data breach exposed patient records via unauthorized access to Quanum LSM; system paused and paper orders advised

Arista patches VeloCloud Orchestrator zero-day exploited in attacks
Iranian hacking group hosts C2 infrastructure in the United States
Meta Fined $25 Billion for Improper Sharing of User Data
New Mexico fines Meta $25 billion for data privacy violations linked to Cambridge Analytica, underscoring impact on enterprises under data-protection laws
Tor Exit Relays Hijacked, Banks Detect Rogue AI Agents, Self-Rebuilding macOS Ransomware
Heartbreaker macOS ransomware self-rebuilds, but a hardcoded AES key and reliance on scarce Rust limit its current threat level
Hackers Breach Enterprise Firewalls and VPNs, Exposing 70,000 Credentials
Global campaign targets exposed edge devices, exposing over 70,000 credentials and enabling persistent access across multiple regions
Mirai Botnet Operators Expand PHP2Shell Attacks as ASLR Bypass Exploits Emerge
Mirai-botnet attempts via PHP2Shell exploit; ASLR bypass revealed, but no confirmed breaches as patches roll out globally
Quest Diagnostics Confirms Data Breach Exposed Patient Records
Quest Diagnostics confirms data breach exposed patient records via unauthorized access to Quanum LSM; system paused and paper orders advised
PHP shares mitigations for new RCE flaw with no patch available
PHP warns of a new remote code execution flaw affecting non-default setups; no patch yet, mitigation includes disabling session.upload_progress.enabled.

PHP Warns of New Unpatched RCE Two Days After PHP2Shell Patches
PHP warns of a new unpatched RCE (CVE-2026-115560) two days after emergency PHP2Shell fixes; recommends disabling session.upload_progress until the next routine patch
The Hacker News: Trusted source for cybersecurity updates
Microsoft says China-aligned Storm-0940 used ARTEX AI agents to accelerate supply-chain attacks, targeting hundreds of organizations across sectors since September 2026
Webinar Explores Hidden AI Risks Threatening Cybersecurity
Live webinar shows five ransomware scenarios targeting backups; immutable storage preserves recovery data and sustains restore paths after attacks
Webinar Warns of Hidden AI Risks Driving a Cybersecurity Crisis
Webinar demonstrates five ransomware scenarios on backup environments and explains how immutable storage safeguards recovery data

eMudhra exits global TLS certificate market after CA signing keys compromised
eMudhra exits global SSL/TLS market after compromise of intermediate CA keys; offers Sectigo certificates and urges review of trust stores beyond browsers
Widespread Token-Spraying Attacks Target Microsoft 365 Email Accounts
Widespread token-spraying attacks target Microsoft 365 accounts to enable email compromise, fueling a major BEC campaign via phishing and stolen session tokens
Attacks on Tech Firms Cause Most Third-Party Data Breach Victims
Third-party breaches via vendors drive the majority of victims, as tech incidents trigger widespread downstream data exposure across supply chains
Attackers Exploit Third VeloCloud Orchestrator Zero-Day in Four Months
Arista patches exploited zero-day in VeloCloud Orchestrator; remote attackers could gain privileged access, compromising confidentiality, integrity and availability of on-prem deployments
Critical flaw in Python Pillow library enables code execution via crafted image
Security update: Pillow flaw allows code execution via crafted EPS filenames; upgrade to version 13.0.0 to mitigate risks across formats
The Hacker News: Index Page of Trusted Cybersecurity News
Exploitation attempts targeting PHP2Shell vulnerabilities were detected from an anonymized IP, traced to Australia, suggesting a single probe prior to public disclosure

HPE patches eight max-severity RCE and authentication bypass flaws in AOS
Hewlett Packard Enterprise patches eight max-severity ArubaOS flaws enabling remote code execution and authentication bypass across AOS-8 and AOS-10

Quest Diagnostics Reports Cyber Breach Affects Some Patient Records
Quest Diagnostics reports unauthorized access to Quanum Lab Services Manager; scope of affected patient records under investigation with external cybersecurity experts assisting

Researchers Demonstrate Node2Shell RCE on Node.js Build via Crafted Brotli Data
Researchers show Node2Shell RCE via crafted Brotli data on the official Node.js build; update to 24.22.1 across 22.x, 24.x and 26.x lines

PHP2Shell Exploit Attacks Hit Millions as Mirai Malware Deployed
Despite multiple exploit attempts, PHP2Shell yields few successful RCE incidents as researchers note botnet Potassium and Mirai variants face execution barriers
Compare ChatGPT, Claude, and Gemini for $59.97
Compare twenty-plus AI models in one tab from a single prompt; ChatPlayground AI Unlimited Plan is on sale for $59.97 (reg. $619)
Compromised TLS Certificates Prompt Security Review
Eight TLS certificates from eMudhra carry extremely weak private keys, raising VPN security concerns and urging users to suspend non-browser TLS communications
Iranian APT Prince of Persia Hosts C2 in U.S. for First Time Since 2016
Iranian-linked Prince of Persia resumes operations with a US-based C&C server, signaling renewed activity after a three-month downtime amid regional cyber tensions

AI Notetaker Risks Spreading Across Sectors
AI notetakers move from meetings to wearables, forcing policies on consent, retention, and vendor access to protect privacy and security

The Mythos moment has passed; cybersecurity faces the hard work ahead
AI-powered cyberattacks accelerate; organizations must speed patching and adopt exposure management to outpace exploits
Network FinOps Helps Control Connectivity and Cloud Costs
FinOps for networks ties visibility and cost allocation to reduce connectivity and egress charges across hybrid and multi-cloud setups
Why CIOs and CHROs Should Partner Strategically
AI reshapes HR, pushing CIOs and CHROs to partner strategically to design work by outcomes and govern the new workforce
Cyber-Attack: Guidance on Communicating with Staff, Customers and Regulators
Crisis messaging after a cyber-attack to staff, customers and regulators shapes outcomes; missteps can erode trust and worsen impact

eMudhra Exits Global SSL/TLS Market After 8 Intermediate CA Keys Easily Guessed
eMudhra to exit global SSL/TLS after discovery of eight easily guessable intermediate CA keys; affected customers to receive free replacements as trust shifts

ThreatsDay AI secrets leak, PingCAP theft, Laravel auth bypass and 21 more
Phishing hits Bluesky as credential and data exposure mount across vendors; Laravel and Signal reveal critical auth, RCE and call-hang vulnerabilities
China-linked actor tied to ConnectWise Cloud Backup attack
China-nexus group linked to ConnectWise Cloud Backup attack used AI to scale strikes on hundreds of Microsoft 365 users

Railway warns developers to rotate secrets after potential breach
Railway pauses deployments after detecting unauthorized access to encrypted environment variables; users are urged to rotate secrets and monitor logs for unusual activity

Two CVSS 9.0 Linux KSMBD RCE Flaws Revealed on Public Lists Before Kernel Patch
Two remote-code-execution flaws in Linux KSMBD, CVSS 9.0, disclosed publicly before kernel fixes, leaving unpatched servers vulnerable
Capcom confirms data breach impacts 11.7 million accounts
Capcom confirms CAPCOM ID breach exposed over 11.7 million emails; small subset saw birth data and password changes, no credit card data affected

Meta Ordered to Pay $25 Billion for 43 Million Privacy Violations
New Mexico court orders Meta to pay $25 billion for alleged privacy violations linked to Cambridge Analytica, faulting misleading data practices
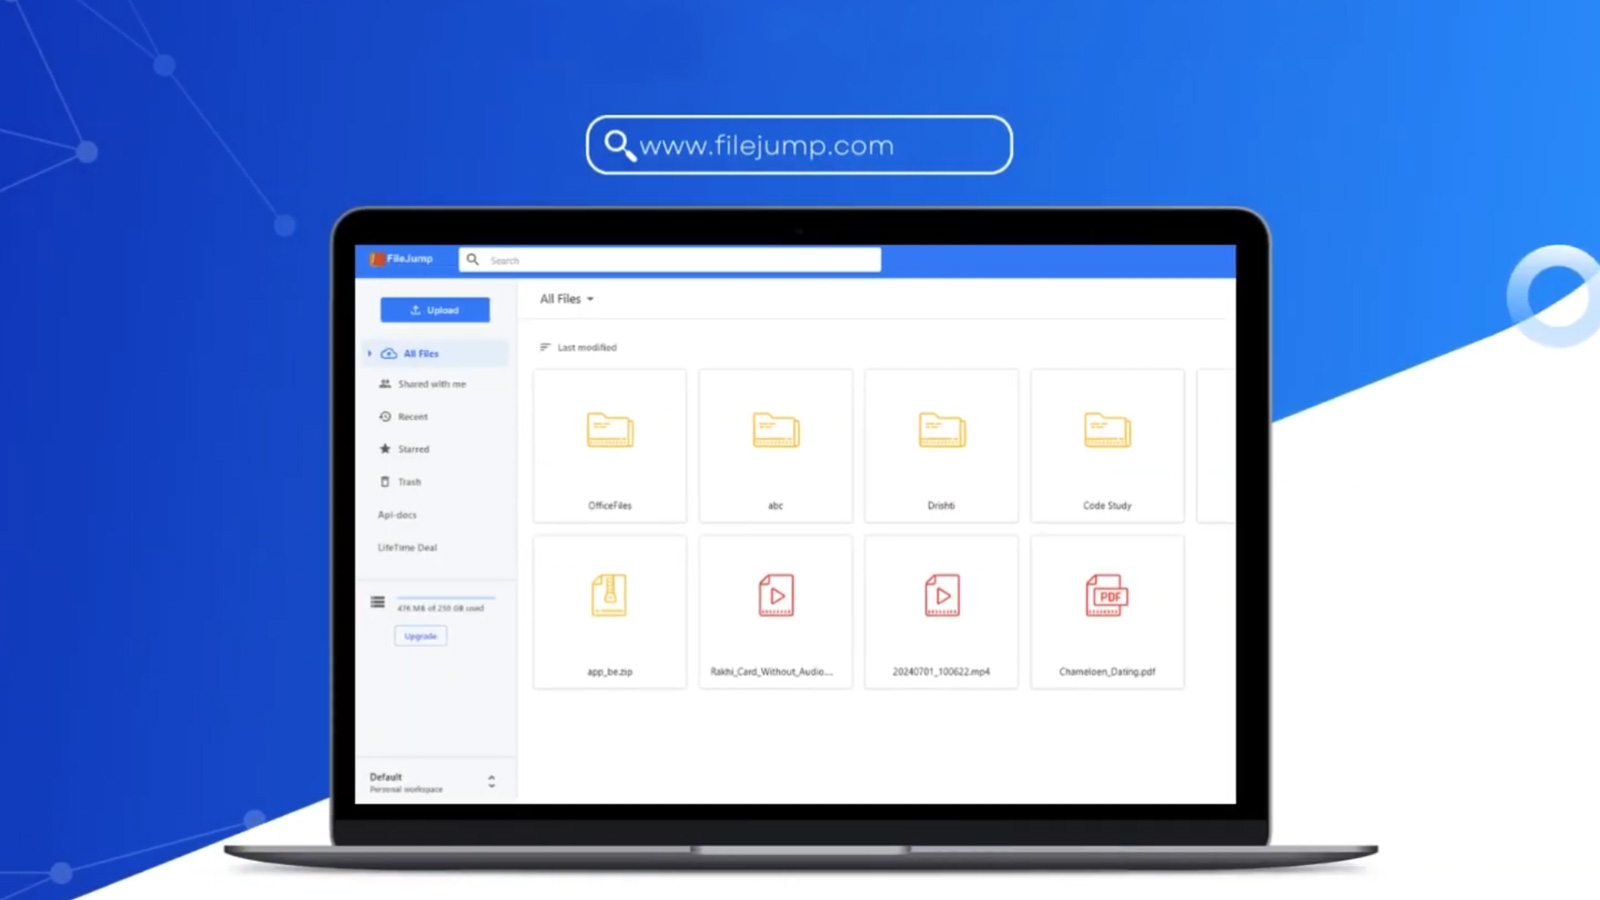
2TB Cloud Storage with Zero-Knowledge Encryption for $59
2TB of cloud storage with zero-knowledge encryption available for a one-time $59, cutting monthly Google One costs though risk if the company goes out of business
The Hacker News: Trusted Cybersecurity News Source Highlights Industry Updates
PHP fixes due at 14:00 UTC on Oct. 21 for two critical flaws; until then, restrict PHP exposure and deploy Cloudflare stopgap rules as a partial safeguard
Serious PHP Vulnerabilities Disclosed and Patched
PHP patches two critical RCE flaws, risking all web deployments; update now to restore security, especially for mod_php setups
Arista patches VeloCloud Orchestrator zero-day exploited in attacks
Arista patches actively exploited zero-day in VeloCloud Orchestrator on‑prem; flaw enables privilege escalation via SQL injection, urging updates and access monitoring
Iranian hacking group hosts C2 infrastructure in the United States
Prince of Persia group hosts C2 on U.S. infrastructure, enabling stealth data exfiltration and surveillance, first Iranian-hosted U.S. operation in over a decade